Table of Contents
- Introduction
- Why RBAC Fails at Scale
- Architectural Principles for Scalable RBAC
- 1. Separate Authentication from Authorization
- 2. Design a Permission Matrix Before Writing Controllers
- 3. Enforce Permissions at the Route or Middleware Level First
- 4. Fetch Roles and Permissions Once Per Request
- 5. Apply Defense-in-Depth for Critical Operations
- 6. Make Multi-Tenant Isolation Structural
- 7. Avoid Hardcoding Role Names
- Recommended RBAC Data Model
- Business Impact of Strong RBAC Architecture
- Conclusion
Introduction
In early-stage SaaS products, access control is often implemented reactively. A basic admin role is added. Then a manager role. Then restrictions are patched into specific endpoints. Initially, this works.
But as the system evolves — more users, more tenants, more features, more compliance requirements — poorly designed Role-Based Access Control (RBAC) becomes a structural liability.
Scaling traffic is a technical challenge.
Scaling authorization complexity is an architectural challenge.
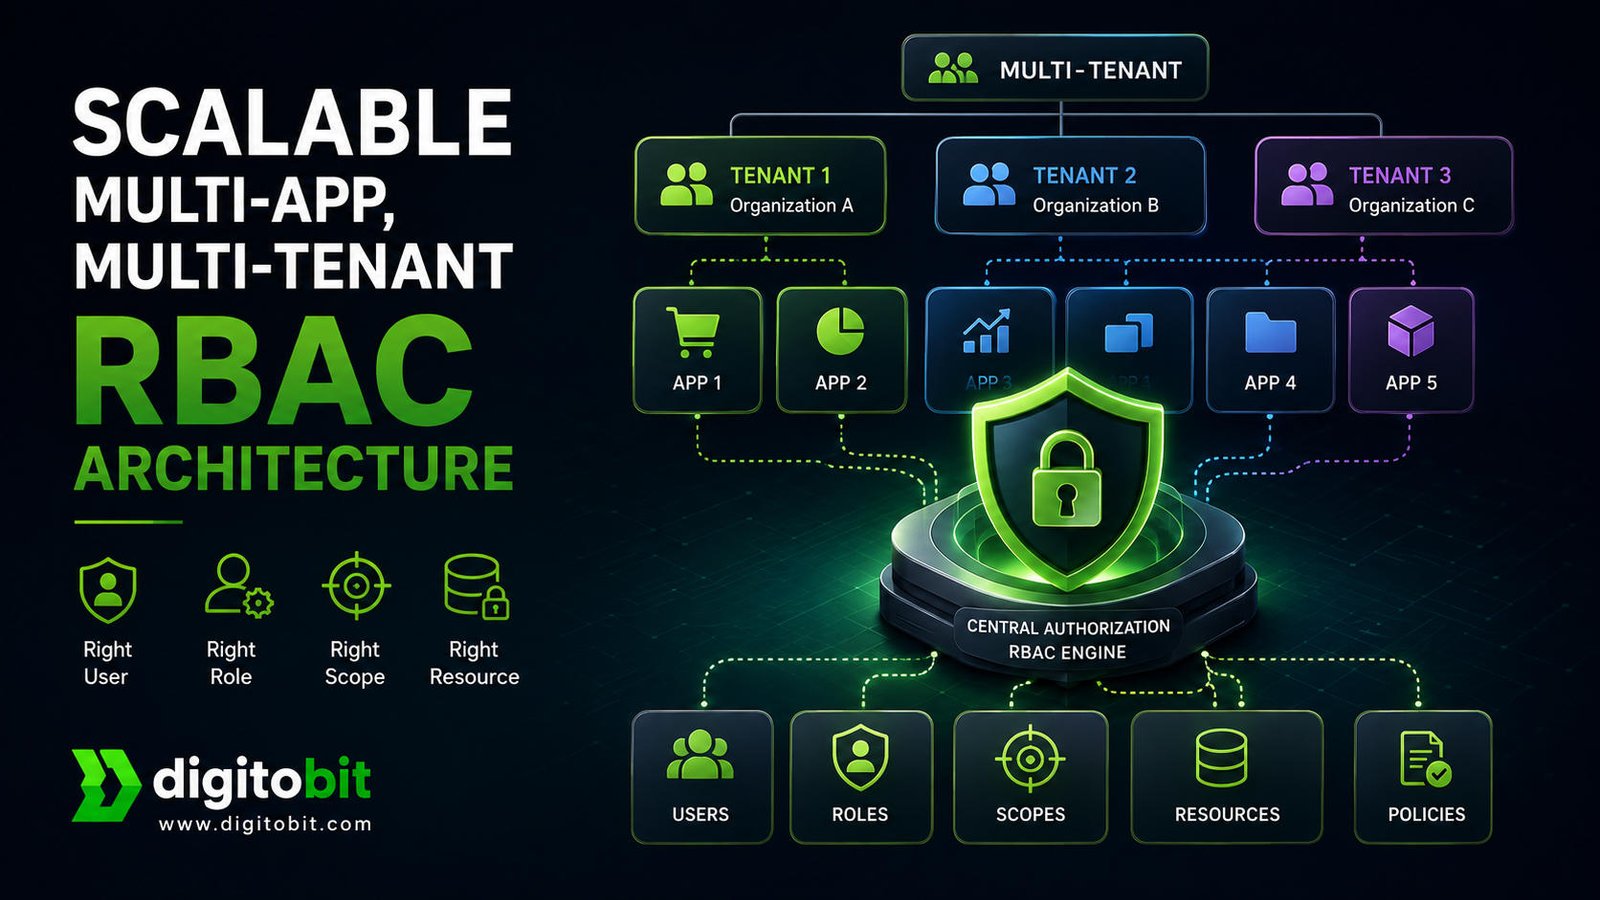
This article explains how to design a scalable Role-Based Access Control (RBAC) system that supports multi-tenant SaaS environments, avoids refactoring chaos, and maintains performance under growth.
Why RBAC Fails at Scale
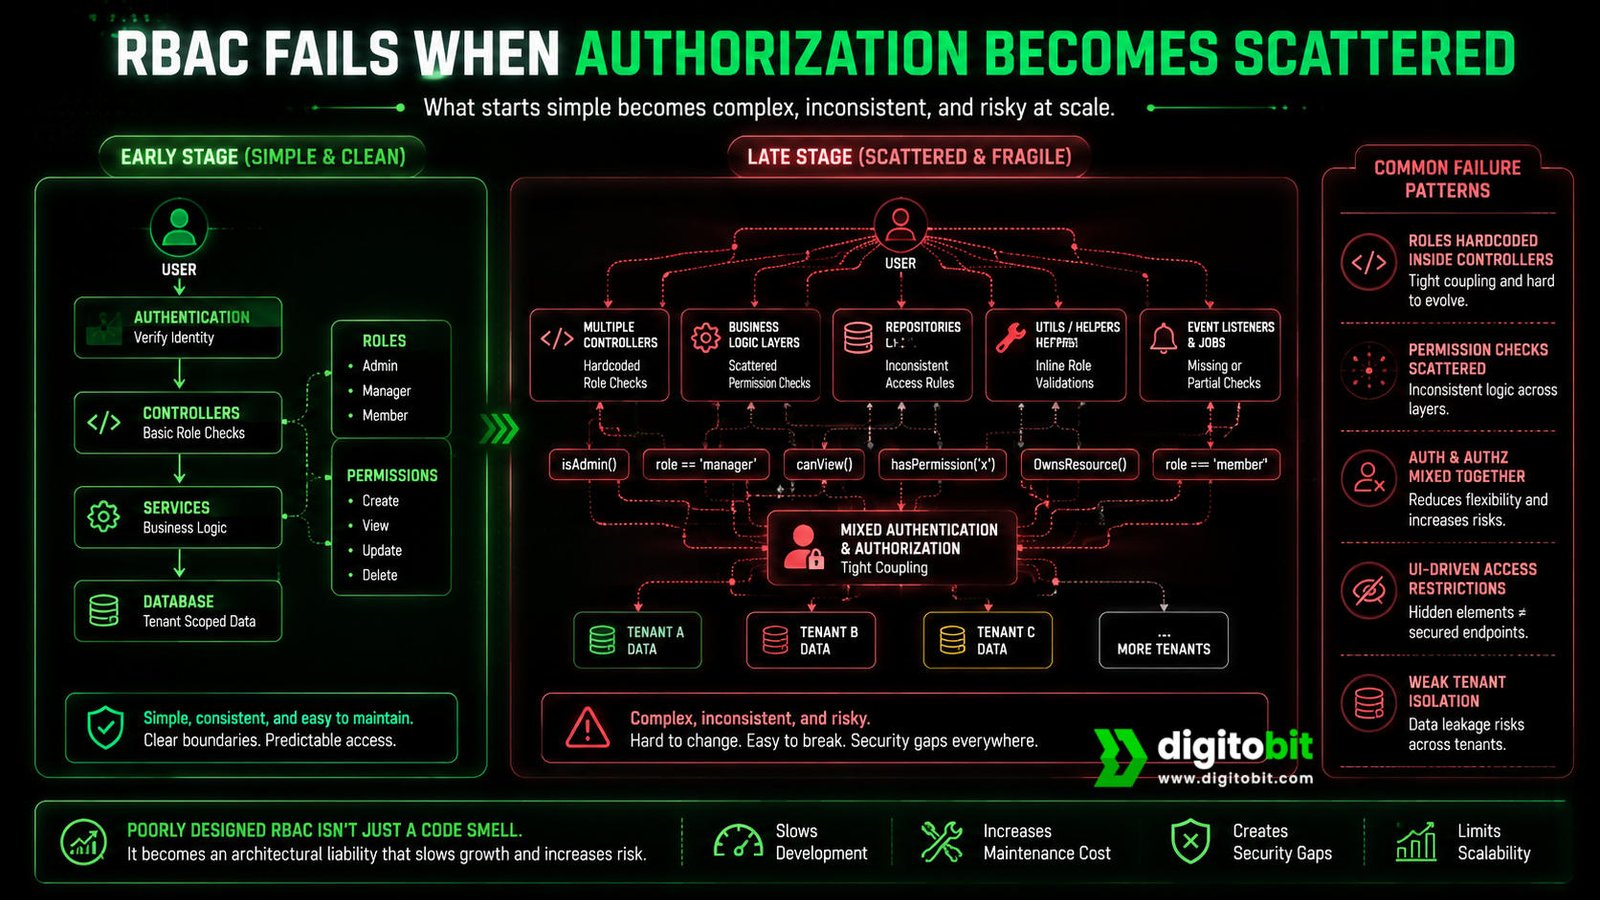
Many systems encounter authorization problems not because the concept of RBAC is flawed, but because of early design shortcuts.
Common Failure Patterns
1. Roles hardcoded inside controllers
Embedding conditional role checks directly into controller logic tightly couples authorization with request handling.
2. Permission checks scattered across business logic
When services, repositories, and controllers all contain independent access checks, policy changes become risky.
3. Authentication and authorization mixed together
Identity verification and capability validation are different concerns. Combining them reduces flexibility.
4. UI-driven access restrictions
Hiding frontend elements without enforcing backend checks creates security gaps.
5. Weak tenant isolation
In multi-tenant systems, inconsistent tenant filtering leads to data exposure risks.
These patterns may survive early MVP stages. They rarely survive enterprise expansion.
Architectural Principles for Scalable RBAC
1. Separate Authentication from Authorization
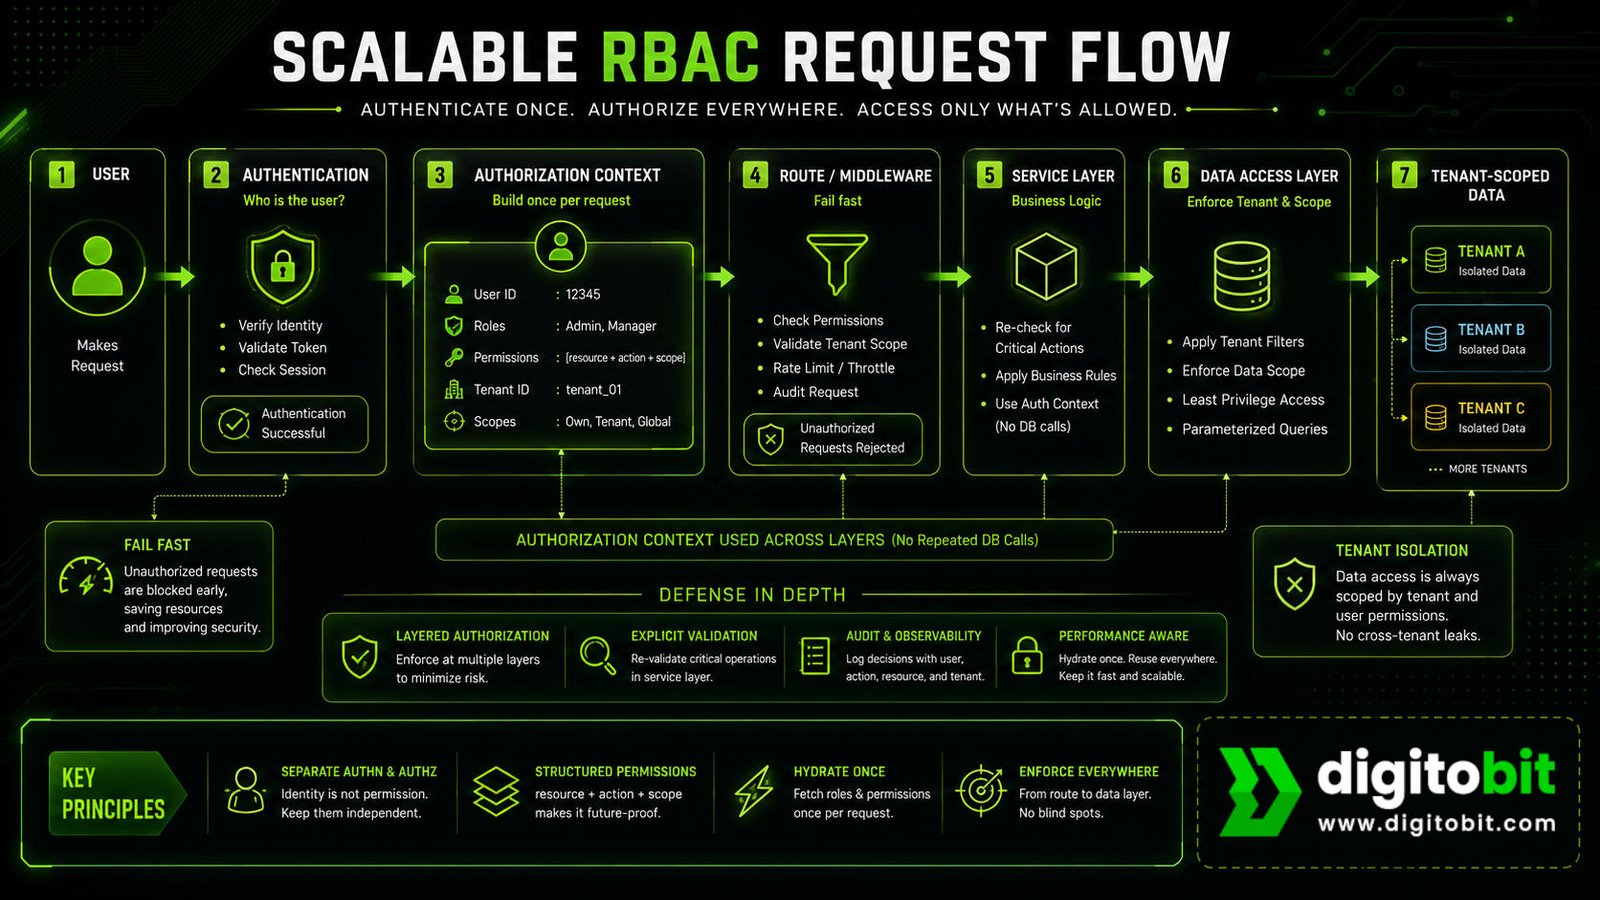
Authentication answers: Who is the user?
Authorization answers: What is the user allowed to do?
Authentication and authorization are separate security concerns, and keeping that distinction clear is important when designing maintainable access-control systems. OWASP Authorization Cheat Sheet
After identity verification, the system should construct a dedicated authorization context. Permission logic must remain independent from session handling or token mechanics.
This separation ensures policy changes do not require rewriting authentication flows.
Summary: Clean boundaries between identity and capability reduce long-term maintenance complexity.
2. Design a Permission Matrix Before Writing Controllers
Before implementing endpoints, define:
- Resources (Orders, Users, Reports, Transactions)
- Actions (Create, View, Update, Delete, Approve)
- Scope (Own, Tenant-wide, Global)
This approach is consistent with the broader RBAC model, where roles represent collections of access authorizations and privileges. NIST RBAC FAQ
A structured permission format such as:
resource + action + scope
allows expansion without refactoring core logic.
A structured permission model aligns with the broader RBAC concept of assigning users to roles that carry defined privileges.
When new roles emerge — regional manager, auditor, branch operator — you assign permissions instead of rewriting code.
Summary: If permissions are structured early, new roles become configuration, not architectural change.
3. Enforce Permissions at the Route or Middleware Level First
Authorization should fail early in the request lifecycle.
Applying permission guards at the route or middleware level ensures unauthorized requests are rejected before reaching controller logic.
Authorization checks should be enforced on the server rather than relying on client-side restrictions alone. OWASP Authorization Cheat Sheet
Benefits include:
- Cleaner controllers
- Predictable request flow
- Centralized logging
- Consistent policy enforcement
Middleware-level enforcement also improves scalability by standardizing authorization behavior across modules or services.
Summary: Fail fast. Keep controllers focused on orchestration, not access validation.
4. Fetch Roles and Permissions Once Per Request
Layered enforcement must not degrade performance.
If permissions are validated at multiple levels — route, middleware, service — and each validation triggers a database query, latency increases unnecessarily.
Instead, on successful authentication:
- Fetch user roles and permissions once
- Build a request-scoped authorization context
- Reuse it throughout the request lifecycle
This approach eliminates redundant database hits while preserving layered security.
Summary: Authorization should be layered. Data retrieval should not be duplicated.
5. Apply Defense-in-Depth for Critical Operations
For sensitive operations such as financial transactions, approvals, or configuration changes, implement an additional permission validation before executing business logic. For particularly sensitive transactions, authorization should be enforced server-side and checked again when the transaction is executed. OWASP Transaction Authorization Cheat Sheet
Example pattern:
$auth->can($user, 'order.update');
This provides:
- Stronger audit trails
- Clear security boundaries
- Safer evolution of policies
Summary: Critical actions deserve explicit validation even after middleware checks.
6. Make Multi-Tenant Isolation Structural
In multi-tenant SaaS systems:
Access = Role + Tenant Boundary + Data Scope
Tenant enforcement must occur at the repository or query layer. It should not depend solely on frontend filtering.
As authorization requirements become more granular, attribute-based access control (ABAC) can complement role-based policies by evaluating attributes associated with the subject, object, requested operation, and environment. NIST SP 800-162 — Guide to Attribute Based Access Control
Super-admin overrides must be controlled and explicit.
Branch-level restrictions must be consistently applied.
Structural tenant isolation dramatically reduces data leakage risk.
Summary: Tenant boundaries are not optional filters. They are foundational architecture.
7. Avoid Hardcoding Role Names
Roles group permissions.
Permissions define authority.
Instead of checking role names in business logic, features should validate permissions.
This enables:
- Enterprise-grade customization
- SaaS tier-based packaging
- Client-specific configurations without core rewrites
Summary: Permissions scale. Role names do not.
Recommended RBAC Data Model
A scalable RBAC schema typically includes:
- users
- roles
- permissions
- role_permission_map
- user_role_map
Operational guidelines:
- Build a centralized authorization service
- Hydrate permissions once per request
- Log sensitive actions with permission context
- Keep business logic independent from role names
Clear architectural boundaries reduce future friction.
Business Impact of Strong RBAC Architecture
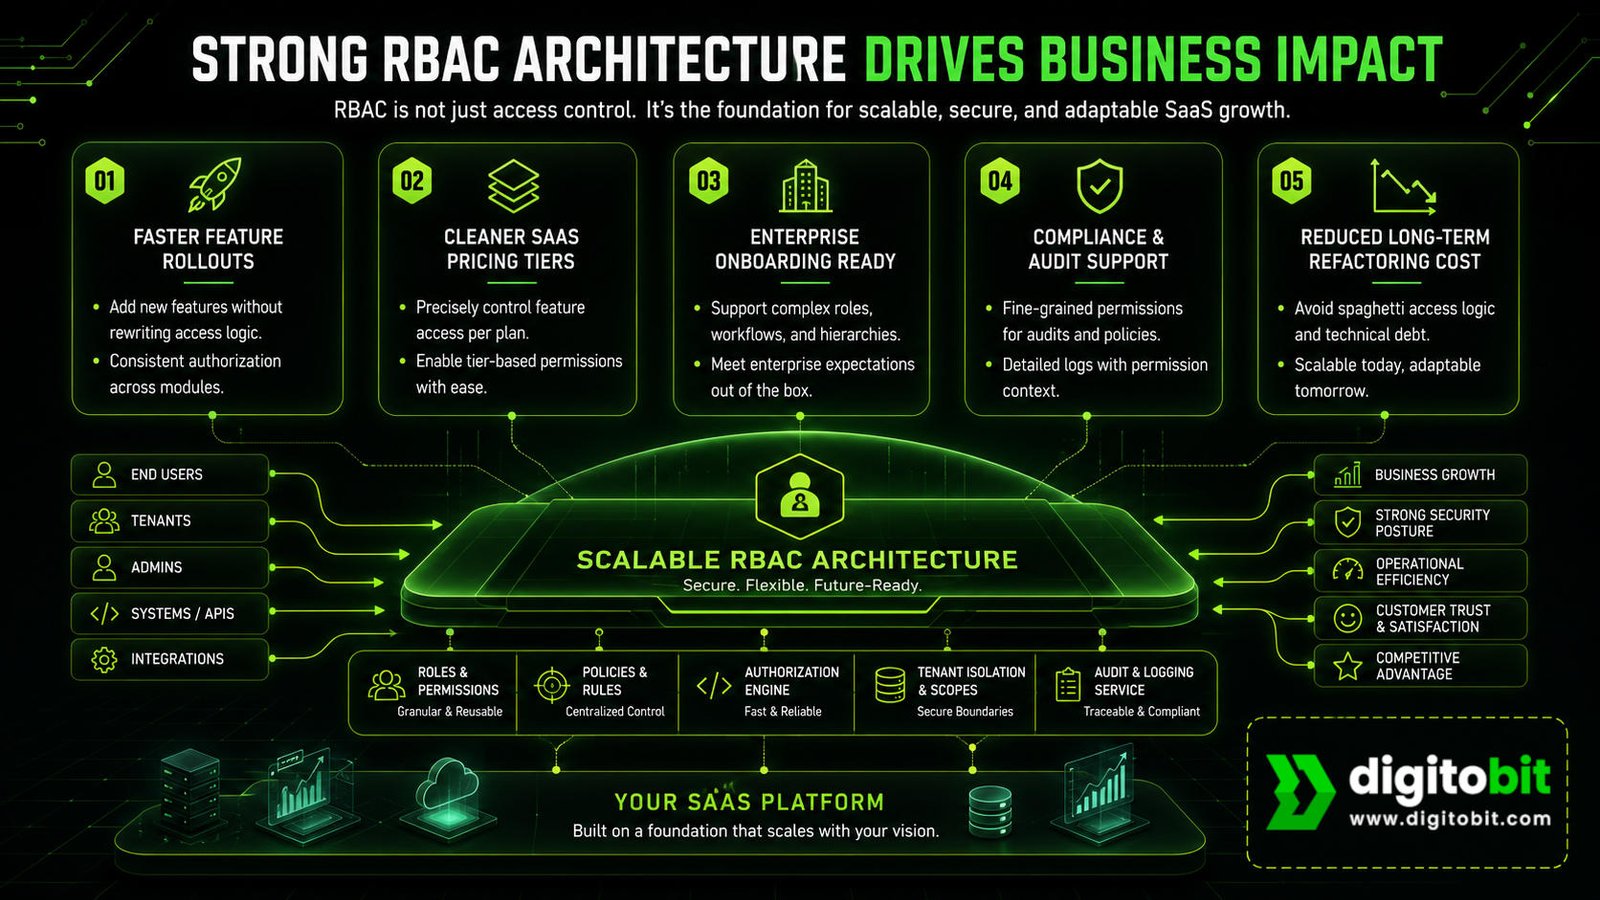
Well-designed Role-Based Access Control enables:
- Faster feature rollout
- Cleaner SaaS pricing tiers
- Enterprise onboarding readiness
- Compliance and audit support
- Reduced long-term refactoring cost
Poor RBAC design results in controller rewrites, fragile access logic, and scalability limitations.
RBAC maturity often marks the difference between a prototype and a production-grade product.
Conclusion
Authorization complexity increases exponentially as tenants, users, and feature combinations grow.
Designing a scalable RBAC system early — with structured permissions, middleware enforcement, tenant isolation, and performance-aware authorization context handling — prevents one of the most expensive categories of refactoring in SaaS systems.
Treat Role-Based Access Control as infrastructure.
Not as a patch.
Author: Neeraj Mourya
Founder, Systems Architect – Digitobit
Specializing in scalable backend architecture and performance-focused SaaS systems